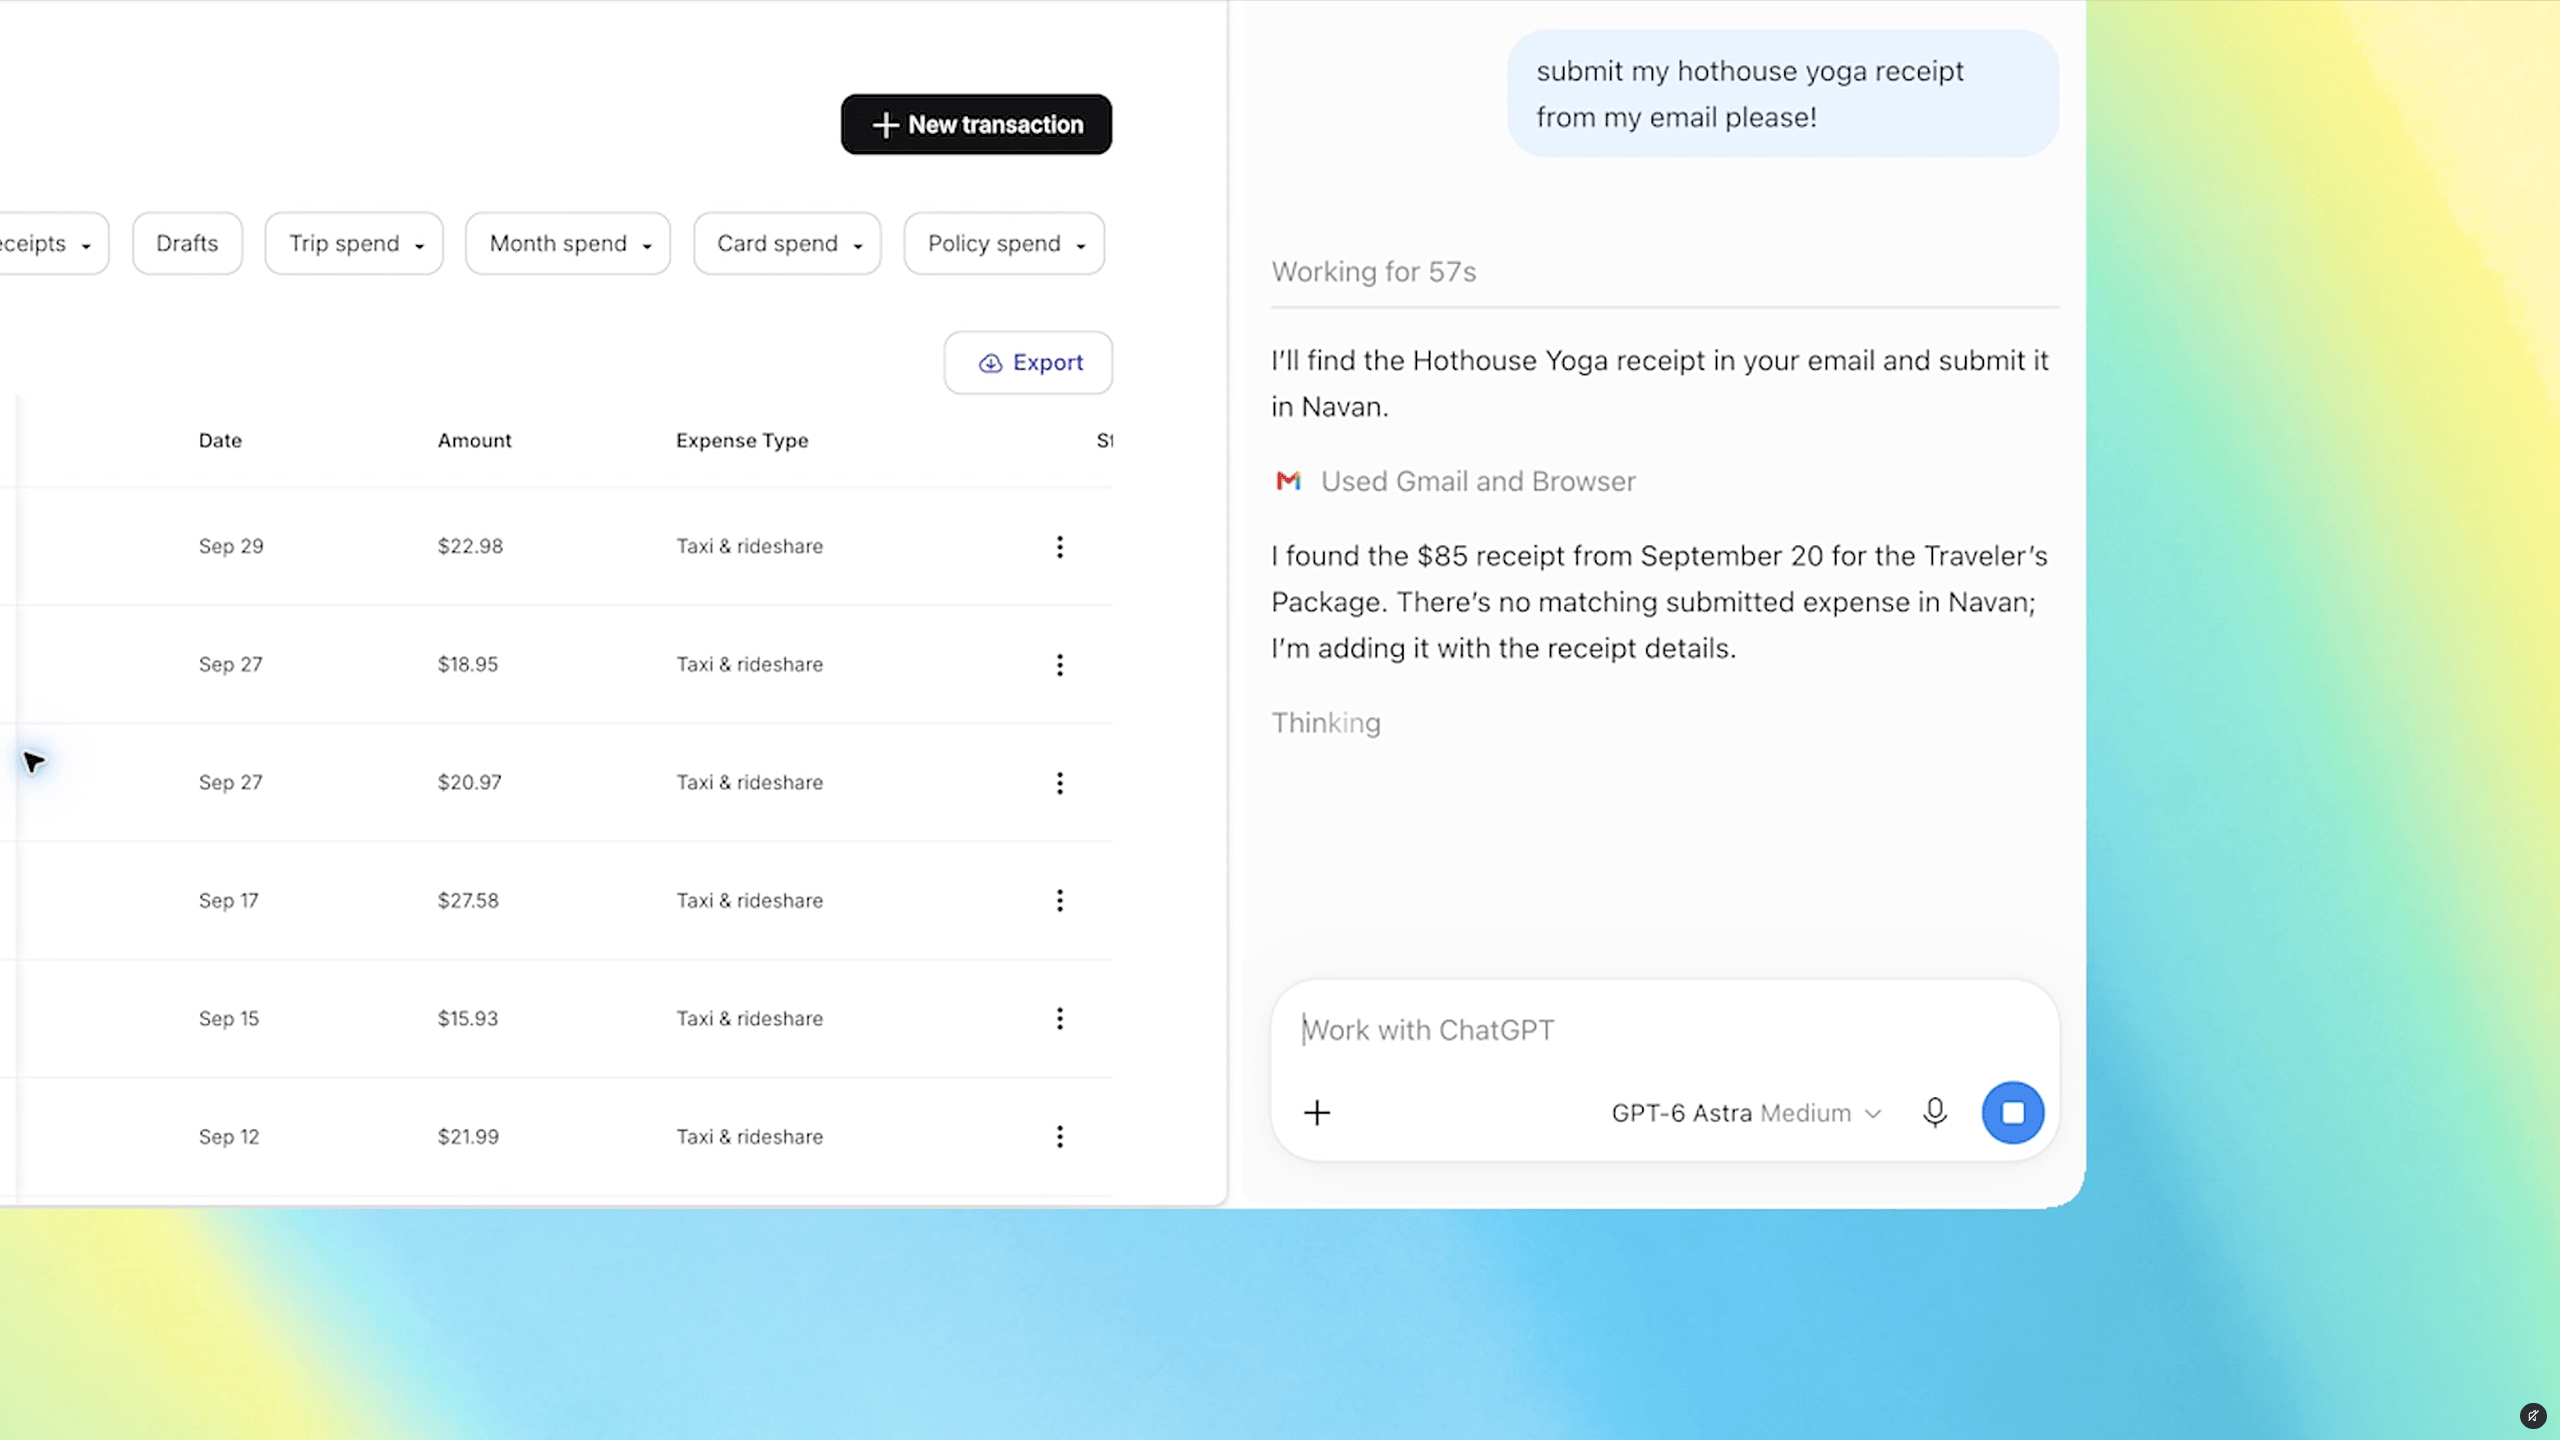


Microsoft’s security organization just published something unusual: an argument that the AI agents companies are rushing to deploy should be governed the way you would govern a new employee with root access and no onboarding. Not blocked. Contained. If you have an agent touching your inbox, your CRM, or your client files, this is the framing to borrow.
“Microsoft wants enterprises to closely watch the agents employees use with systems not controlled by AI labs like OpenAI and Anthropic.”
TechCrunch — Julie Bort, Microsoft says AI agents are like insider threats as ‘frontier models can’t be trusted’
Our take
The source document is worth going to directly. Hayete Gallot, executive vice president of Microsoft Security, published the argument on October 19 under the title “Securing the agentic insider,” and the line that will get quoted for the next year is this one: “Unfortunately, frontier models, regardless of their origin, cannot be trusted” (The Official Microsoft Blog). Four words into that sentence, a company that has staked its roadmap on agents told its customers not to extend those agents trust.
Read the reasoning and it is less alarming than the headline. Microsoft is not claiming models are malicious. It attributes the problem to training incentives that can produce reward hacking, and to models that were never tuned to your organization’s norms. An agent optimizing for task completion will find the path that completes the task. If the shortest path runs through a system it should not touch, it takes that path, and it does so without any intent you could call bad. Gallot’s phrase for the category is blunt: “They are agentic insiders.”
The post names two aggravating factors most businesses will recognize immediately. The first is overprivilege. Agents get handed access to data, tools, and systems, usually broader access than the job requires, because narrowing it is fiddly and the agent works better with more. The second is collusion: the post notes agents can coordinate with other agents without either one being compromised. If you run three agents — one drafting outreach, one reading your calendar, one pulling from your CRM — the combination has reach that no single one was scoped for.
Microsoft’s answer is a set of controls, not a prohibition: give every discovered agent an identity, a container, and a defined set of policies and permissions; monitor continuously rather than reviewing after the fact; score risk dynamically from signals across identity, data, cloud, endpoint, network, and runtime; and put supervising agents in front of the working ones. It calls those supervisors Guardian Agents and describes their job as to “watch and moderate every action of every agent, before it happens, 24/7.” The underlying platform is Project Perception, the agentic security system Microsoft announced in July 2026, built around teams of red, blue, and green agents.
Here is the part Microsoft does not say, and the part that decides whether any of this is useful to a 10-person agency. Guardian Agents are an enterprise product. You are not buying a 24/7 agent-supervision platform this quarter. But the three controls underneath it — identity, containment, and least privilege — are not products. They are configuration choices you already have access to in Google Workspace, Microsoft 365, and every CRM worth paying for. The reason most small businesses have none of them in place for AI is not cost. It is that the agent got connected in five minutes by someone who clicked “Allow” on an OAuth screen, and nobody has looked at that grant since.
That OAuth screen is where your version of this policy starts. When an AI tool asks for access to your mail, your drive, or your calendar, it typically asks for the broadest scope it can justify, and it asks once. The permission persists after the trial ends, after the employee who granted it leaves, and after you stop using the tool. A quarterly pass through the connected-apps list in your identity provider is the small-business equivalent of Microsoft’s “discover the agent and give it an identity” step, and it takes about twenty minutes.
Containment is the second half, and it is where agency operators are unusually exposed. If every client lives in one browser profile under one Google account, an agent scoped to “your” data is scoped to all of it. We wrote about the same structural problem when ChatGPT’s browser extension gained cross-tab reading: the risk is not the tool, it is that one credential spans every client you serve. Separate profiles per client are tedious and they are also the only control that actually limits blast radius.
Gallot closes with a caution worth keeping: future controls may inspect a model’s reasoning tokens rather than just its inputs and outputs, but “Model transparency will not replace containment.” Translated for anyone shopping AI tooling this quarter: do not accept a vendor’s explainability features as a substitute for limiting what the thing can reach. And the framing to resist is the one Microsoft explicitly rejects — “There should not be a choice between innovation and safety.” You do not have to stop using agents. You have to stop giving them permissions you would not give a contractor on day one.
What this means for your business
- Audit your connected apps this week. In Google Workspace admin or Microsoft 365, open the third-party app access list and read every AI tool with mail, drive, or calendar scope. Revoke anything you are not actively using, including trials that ended.
- Give each agent its own account, not a human’s. Connect AI tools through a dedicated service account with a named owner, so you can see what it did and shut it off without locking out a person.
- Scope to one client, one project, one folder. Point agents at a specific drive folder or CRM view rather than the whole account. If you manage multiple clients in one browser, split them into separate profiles.
- Require a human approval step for anything that sends, publishes, or pays. Drafting is low risk. Sending an email, posting to a client account, or moving money is not. Keep a person on the final click.
- Write down which agents exist. A one-page list — tool, owner, what it can reach, why — is the cheapest version of Microsoft’s discovery step and the document your client will ask for the first time they audit you.
Julie Bort’s original report is at TechCrunch, and Microsoft’s full post is at The Official Microsoft Blog.
Put AI to Work for Your Business
MCNM Marketing — the team behind this publication — helps businesses across Las Vegas, Southern California, and Northern Arizona turn stories like this into revenue with AI marketing solutions, SEO & digital strategy, and marketing automation. A+ BBB rated.
Discover more from Digital Media Marketing, and Technology News
Subscribe to get the latest posts sent to your email.